AI Governance
Responsible AI Adoption: Building a Governance Framework
A workable governance program connects an AI inventory, risk review, human oversight, and ongoing monitoring.
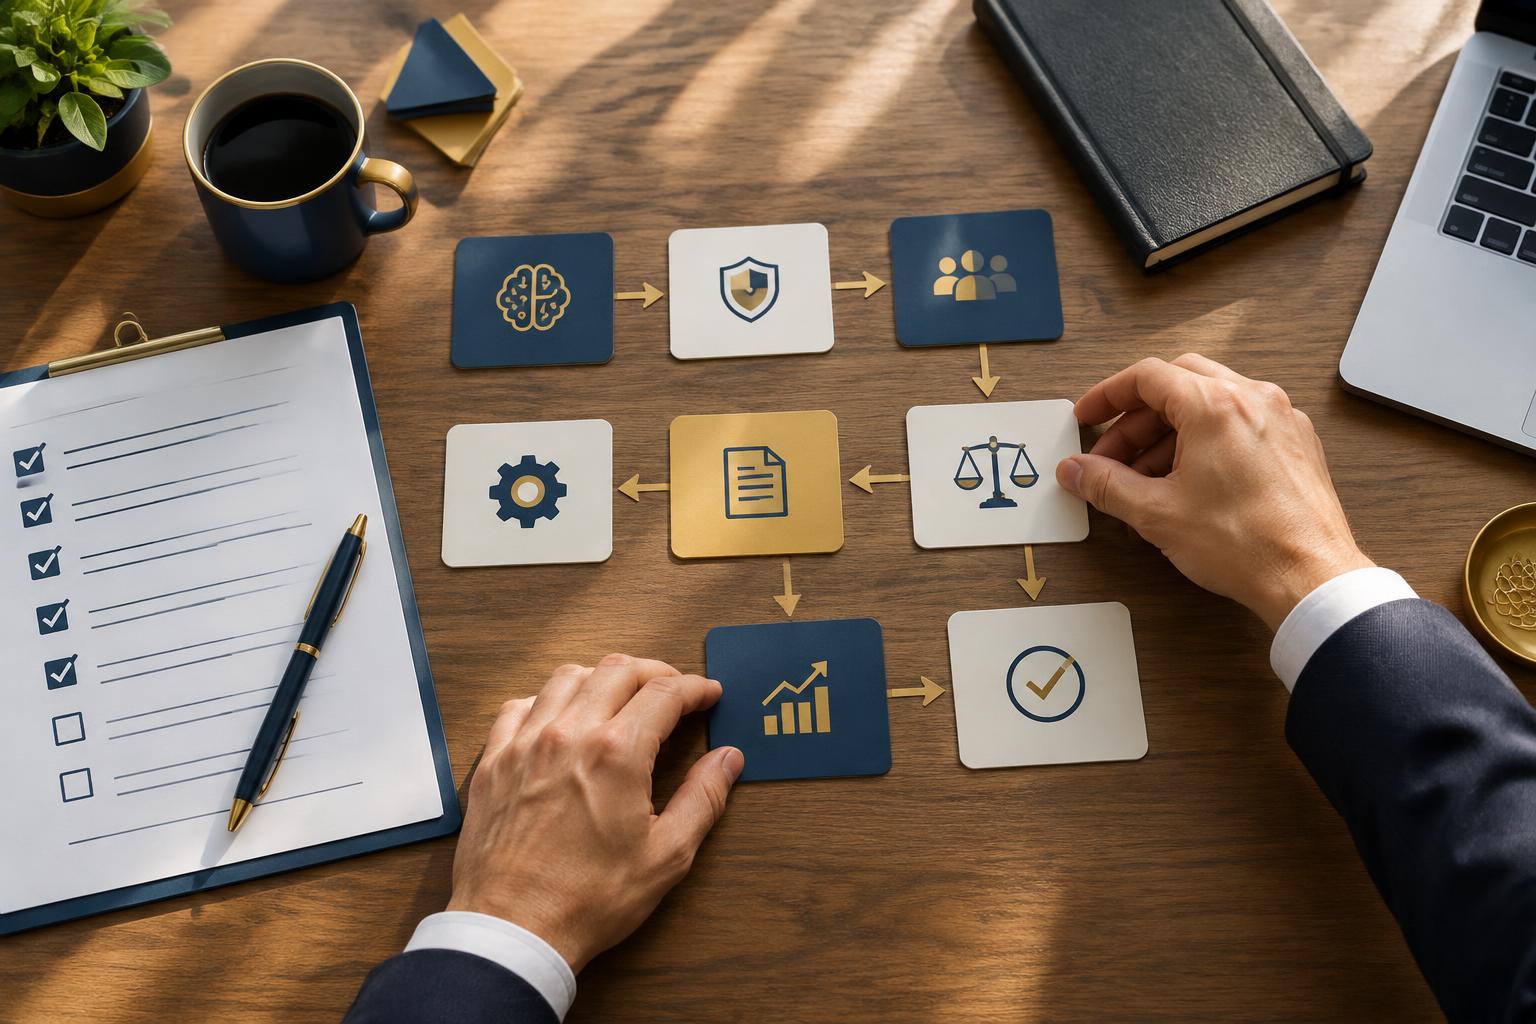
Responsible AI is an operating discipline, not a slogan. Organizations need a practical way to decide which uses are acceptable, who approves them, and how systems are monitored after deployment. Governance should support informed adoption while making harmful or unjustified uses harder to pursue.
Establish ownership and an inventory
Create an inventory of AI-enabled systems, including features provided by vendors. Record the purpose, business owner, affected people, data sources, and deployment status. Keep the inventory current as tools and uses change.
Assign accountability for the business outcome and for risk review. A cross-functional group can advise, but a committee should not obscure who can approve a use, accept residual risk, or stop deployment.
Review impact in context
Assess the consequences of an incorrect, biased, or unavailable output. Consider whether a person can challenge the result and whether the system affects access to opportunities or essential services. The same model may present different risks in different workflows.
The NIST AI Risk Management Framework organizes risk work around Govern, Map, Measure, and Manage. It is a useful structure for defining responsibilities and evaluating context; using it does not by itself certify compliance with any law.
Translate principles into operational controls
Specify approved data, access permissions, evaluation requirements, and human review points. Define what reviewers must check and what authority they have to reject an output. A nominal human in the loop is not meaningful oversight if they lack time, information, or decision rights.
Document the intended use and limitations in language the users understand. Train staff on escalation and on situations where the system should not be used.
- Record intended use and prohibited uses.
- Evaluate representative cases and foreseeable harms.
- Identify review, escalation, and appeal mechanisms.
- Approve changes before expanding scope or access.
Monitor and revisit the decision
Track errors, user complaints, unexpected behavior, and changes in performance. Review vendor updates and data changes that could affect prior evaluations. The approval decision needs to be revisited when the use case changes materially.
Keep evidence of evaluations, decisions, and corrective action. Seek appropriate legal advice for obligations that apply to your sector, location, and use case rather than treating a general framework as a substitute for that analysis.
Further reading
General educational guidance; not legal advice. Requirements depend on your organization, sector, and use case.